Published: September 15, 2026
Tags:
VMware,
vCenter,
ransomware,
vulnerabilities,
CISA,
CVE-2026-59310
Category:
vulnerabilidades
 Original image source: bleepstatic.com
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning that ransomware gangs are now actively exploiting a critical VMware vCenter vulnerability, identified as CVE-2026-59310, which was patched in July. This development comes …
Published: September 10, 2026
Tags:
artificial intelligence,
papercut ng/mf,
vulnerabilities,
exploitation campaign,
threat intelligence
Category:
inteligencia-de-amenazas
 Original image source: bleepstatic.com
A threat actor, presumably Russian-speaking, has launched an unprecedented global exploitation campaign, using hundreds of artificial intelligence (AI) agents to compromise vulnerable PaperCut NG/MF servers. The campaign, detected by threat intelligence …
Published: September 3, 2026
Tags:
zero-day,
Crowdstrike Falcon,
privilege escalation,
Chaotic Eclipse,
exploit
Category:
vulnerabilidades
Chaotic Eclipse Unveils FalconFlank Zero-Day for Crowdstrike Falcon
Security researcher Chaotic Eclipse, also known by aliases like INFINITE NIGHTMARE, MSNightmare, and Nightmare-Eclipse, has publicly released “FalconFlank,” a proof-of-concept (PoC) exploit for a zero-day privilege …
Published: August 14, 2026
Tags:
CDP,
Chrome,
Edge,
Post-exploitation,
Cookie Theft,
Threat Hunting,
SpecterOps
Category:
threat-research
Post-exploitation technique using Chrome DevTools Protocol (CDP) inside Chrome/Edge on Windows to steal cookies, passwords, and authenticated sessions after initial access.
Published: August 10, 2026
Tags:
AI PC,
NPU,
Artificial intelligence,
ASUS,
hardware
Category:
artificial-intelligence
 Original image source: itseller.cl
The arrival of AI PCs is marking a turning point in the way companies approach their end-user infrastructure. In this new panorama, components such as the NPU (Neural Processing Unit) are emerging as essential elements to execute Artificial Intelligence (AI) …
Published: June 16, 2026
Tags:
Chile Cybersecurity Framework Law,
ANCI,
Business Cybersecurity,
Cyber Risk Chile,
Cybersecurity Regulatory Compliance
Category:
análisis-de-malware
In the current digital environment, Enterprise Cybersecurity is no longer an exclusive issue for IT departments. For managers, today it represents a critical variable for financial survival.
Ignoring Cybersecurity Regulatory Compliance not only exposes the organization to fines, but can …
Published: May 12, 2026
Tags:
cybersecurity,
chili,
law 21663,
regulation,
human resources
Category:
regulatorio
The recent Cybersecurity Framework Law (Law 21,663) in Chile establishes a significant regulatory milestone, creating a general framework for digital protection that transcends traditionally regulated sectors and reaches a greater number of private institutions. This new regulation seeks to address …
Published: May 6, 2026
Tags:
MuddyWater,
ransomware,
false-flag,
Microsoft Teams,
advanced-persistent-threat
Category:
inteligencia-de-amenazas

The Iranian state-sponsored hacking group known as MuddyWater (also as Mango Sandstorm, Seedworm, and Static Kitten) has been implicated in a “false flag” ransomware attack, according to a report from Rapid7. This incident, observed in early 2026, shows increasing sophistication and an …
Published: May 5, 2026
Tags:
cyber attacks,
business reputation,
trust,
incident response,
Latin America
Category:
respuesta-a-incidentes
 Image original source: bloka.red
Cyberattacks go beyond financial costs, generating an “invisible cost” that seriously impacts the reputation and trust of companies, especially in Latin America. The lack of incident response plans in the region amplifies this problem, turning a safety …
Published: May 2, 2026
Tags:
Trellix,
security breach,
source code,
incident,
FireEye
Category:
respuesta-a-incidentes

Cybersecurity company Trellix has announced that it suffered a breach that allowed unauthorized access to a “portion” of its source code.
Incident Details
Trellix reported having “recently” identified the compromise of its source code repository. Immediately following the …
Published: May 1, 2026
Tags:
cybercrime,
cyber attacks,
phishing,
vishing,
SaaS,
operational security
Category:
inteligencia-de-amenazas

Cybersecurity researchers warn about the operation of two cybercriminal groups, Cordial Spider and Snarky Spider, which are executing data theft and extortion attacks in a “rapid and high-impact” manner, operating almost exclusively within SaaS (Software as a Service) environments and …
Published: April 23, 2026
Tags:
compliance,
Chilean regulations,
cybersecurity,
data protection,
risk management
Category:
cumplimiento
The New Regulatory Panorama in Chile 2025-2026
Chile is undergoing a profound regulatory transformation between 2025 and 2026, which directly impacts cybersecurity, data protection, modernization of procedures and environmental sustainability. This change represents a turning point for companies, …
Published: April 22, 2026
Tags:
anthropic,
claude-mythos,
vulnerabilities,
cybersecurity,
artificial-intelligence
Category:
artificial-intelligence
Anthropic, the artificial intelligence company, has confirmed that its new cybersecurity expert language model, Claude Mythos, has been compromised. Despite having restricted access to the tool due to its potential danger, AI has fallen into unauthorized hands, generating serious concern in the …
Published: April 14, 2026
Tags:
Corporate Cybersecurity,
Cyber Risk Chile,
Chile Cybersecurity Framework Law,
ANCI,
Cybersecurity Compliance
Category:
cybersecurity
Discover how Shadow AI impacts corporate cybersecurity in Chile. We analyze data risks, compliance under the Cybersecurity Framework Law, and strategies for secure management.
Published: March 2, 2026
Tags:
google chrome,
vulnerability,
cve-2026-0628,
gemini ai,
extensions,
cve,
browser security
Category:
vulnerabilities

Cybersecurity researchers have revealed details about a critical vulnerability already patched in Google Chrome that could have allowed attackers to elevate privileges and gain access to local files on the victim’s system.
The vulnerability, tracked as CVE-2026-0628 and with a CVSS score of …
Published: February 26, 2026
Tags:
Aeternum C2,
botnet,
blockchain,
threat-intelligence,
malware-analysis,
crimeware-as-a-service
Category:
inteligencia-de-amenazas

Cybersecurity researchers have revealed details about a new botnet loader called Aeternum C2, which uses a blockchain-based command and control (C2) infrastructure to resist takedown efforts. Instead of relying on traditional servers or domains, Aeternum stores its instructions on the public …
Published: February 23, 2026
Tags:
malware-analysis,
obfuscation,
threat-campaign,
JScript,
Remcos-RAT
Category:
análisis-de-malware
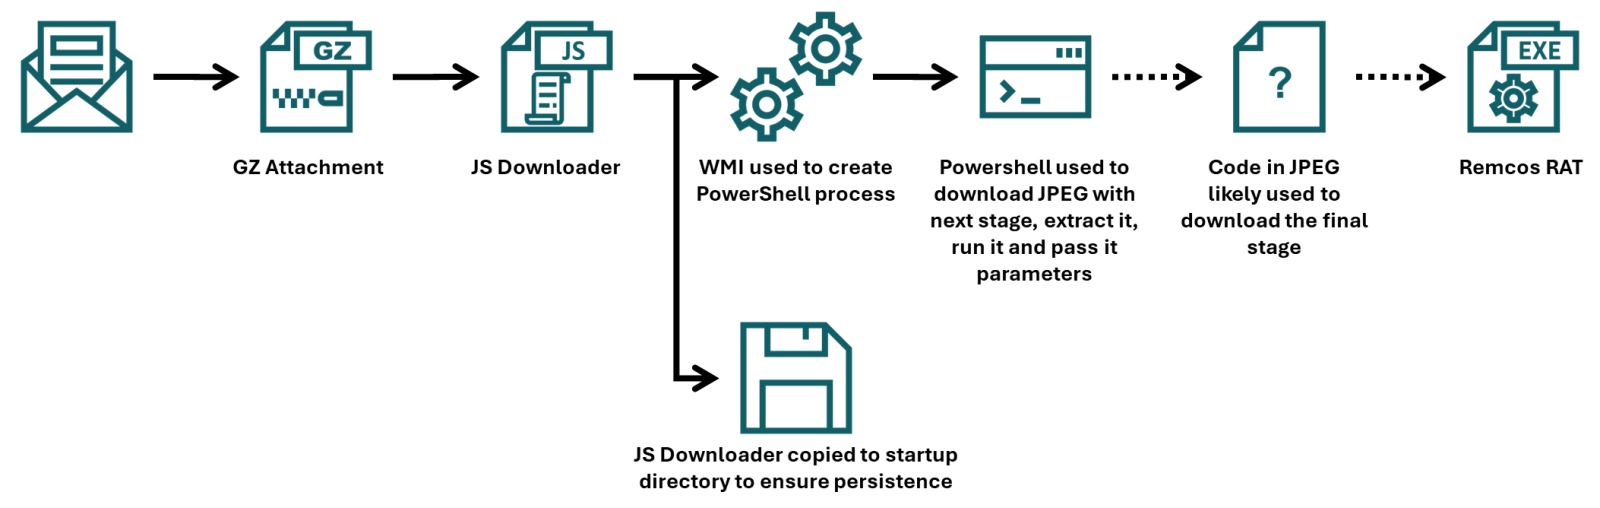
This article presents a detailed analysis of a recent malware campaign that uses advanced obfuscation techniques to evade detection. The infection chain begins with a JScript script attached to a phishing email and culminates with the download of Remcos RAT. The analysis focuses on the obfuscation …
Published: January 27, 2026
Tags:
EDR,
NDR,
artificial intelligence,
advanced threats,
network security,
security operations
Category:
operaciones-de-seguridad

Cybersecurity faces a constant challenge: innovation from adversaries. The rise of offensive artificial intelligence (AI) is transforming attack strategies, making them harder to detect. Threat actors use large language models (LLMs) to hide code and generate malicious scripts on the fly. These …
Published: January 26, 2026
Tags:
cloudflare,
bgp,
route leak,
network-security,
configuration-management,
ipv6
Category:
gestión-de-configuración
Cloudflare has shared details about a recent Border Gateway Protocol (BGP) route leak incident that affected IPv6 traffic for 25 minutes. The incident caused significant congestion, packet loss, and the drop of approximately 12 Gbps of traffic, impacting external networks beyond Cloudflare’s …
Published: January 26, 2026
Tags:
Fortinet,
FortiGate,
Vulnerability,
CVE-2025-59718,
FortiCloud SSO
Category:
vulnerabilities

Fortinet has confirmed that it is working to fully fix a FortiCloud SSO authentication bypass vulnerability, following reports of new exploit activity on firewalls that had already been fully patched.
Discovery of New Attack Route
Carl Windsor, CISO of Fortinet, reported that cases of exploitation …
Published: January 26, 2026
Tags:
zero-day,
microsoft office,
vulnerabilities,
cve-2026-21509,
patch management
Category:
vulnerabilities
Microsoft has released emergency out-of-band security updates to patch a high-severity zero-day vulnerability in Microsoft Office that is being actively exploited in attacks.
The vulnerability, tracked as CVE-2026-21509, is a security feature bypass that affects multiple versions of Office, …
Published: January 26, 2026
Tags:
threat-intelligence,
phishing,
malware-analysis,
Blackmoon,
cyber-espionage
Category:
threat-intelligence

Cybersecurity researchers have uncovered an ongoing cyber espionage campaign specifically targeting users in India. The attack utilizes a multi-stage backdoor and leverages sophisticated evasion techniques to achieve persistent access and data exfiltration from compromised systems.
Initial Attack …
Published: January 26, 2026
Tags:
threat-intelligence,
phishing,
remote-monitoring-management,
logmein,
persistence
Category:
inteligencia-de-amenazas

Cybersecurity researchers have revealed details of a new dual-vector attack campaign that leverages stolen credentials to deploy legitimate Remote Monitoring and Management (RMM) software. The goal is to establish persistent remote access to the compromised hosts.
According to researchers at …
Published: January 26, 2026
Tags:
Peck Birdy,
APT,
SHADOW-VOID-044,
SHADOW-EARTH-045,
threat-intelligence,
malware-analysis
Category:
inteligencia-de-amenazas
This report details two threat campaigns using the PeckBirdy JavaScript framework, attributed to China-aligned advanced persistent threat (APT) actors. The campaigns, temporarily named SHADOW-VOID-044 and SHADOW-EARTH-045, demonstrate the increasing sophistication and adaptability of these groups. …
Published: January 26, 2026
Tags:
artificial intelligence,
child safety,
data privacy,
digital education,
psychological risks
Category:
concienciación-en-seguridad
The use of artificial intelligence (AI) chatbots has become widespread rapidly, with platforms like ChatGPT reaching hundreds of millions of users, many of them young people. A 2025 UK study revealed that almost two-thirds (64%) of children use these tools. Despite its popularity, the frequent use …
Published: January 26, 2026
Tags:
Sandworm,
DynoWiper,
Poland,
cyber attack,
critical infrastructure,
APT,
ESET
Category:
inteligencia-de-amenazas

The Russian state-linked Sandworm hacking group has been identified as responsible for what is described as the “largest cyberattack” targeting Poland’s power system in the last week of December 2025. Although the attack was detected and neutralized without causing any disruption, …
Published: January 26, 2026
Tags:
shinyhunters,
crunchbase,
data-breach,
incident-response,
extortion,
leak
Category:
respuesta-a-incidentes
Crunchbase has confirmed a cybersecurity incident following claims by the cybercriminal group ShinyHunters, which claims to have stolen more than 2 million personal records from its systems.
ShinyHunters leaked a 402MB zip file on its Tor website, stating that the data release was due to a failed …
Published: January 19, 2026
Tags:
ransomware,
data breach,
Ingram Micro,
SafePay,
threat intelligence
Category:
inteligencia-de-amenazas
Ingram Micro Suffers Data Breach Due to Ransomware Attack
Information technology giant Ingram Micro has confirmed a data breach affecting more than 42,000 people, the result of a ransomware attack detected in July 2025. The company, a global B2B service provider and technology distributor with net …
Published: January 16, 2026
Tags:
malicious-extensions,
prompt-poaching,
security-ai,
data-exfiltration,
chrome-web-store
Category:
análisis-de-malware

Cybersecurity researchers have discovered two new malicious extensions in the Chrome Web Store designed to exfiltrate OpenAI ChatGPT and DeepSeek conversations, along with browsing data, to servers under the attackers’ control. This type of attack, which uses browser extensions to stealthily …
Published: January 15, 2026
Tags:
palo alto networks,
globalprotect,
pan-os,
cve-2026-0227,
denial of service
Category:
vulnerabilities

Palo Alto Networks has released a major security update to address a high severity vulnerability affecting its GlobalProtect Gateway and Portal software. The company has confirmed the existence of a proof-of-concept (PoC) exploit for this flaw, underscoring the urgency of patching.
Vulnerability …
Published: January 14, 2026
Tags:
threat-intelligence,
malware-analysis,
Ukraine,
phishing,
void-blizzard
Category:
inteligencia-de-amenazas

Ukraine’s Computer Emergency Response Team (CERT-UA) has revealed details of a series of new cyberattacks targeting its defense forces and state institutions. These attacks, which took place between October and December 2025, involve various intrusion techniques and several malware families, …
Published: January 13, 2026
Tags:
Endesa,
data breach,
threat actor,
cybercrime forum,
Spain
Category:
respuesta-a-incidentes
Endesa Confirms Security Incident Following Threat Actor Statement
Spanish energy company Endesa has confirmed a security incident that resulted in unauthorized access to its trading platform, compromising customer data. Endesa is the largest electricity supplier in Spain, serving more than 10 …
Published: January 7, 2026
Tags:
Veeam,
Backup & Replication,
vulnerabilities,
CER,
security patches
Category:
vulnerabilities

Veeam has released a series of critical security updates to its Backup & Replication software, addressing multiple flaws, including a vulnerability classified as “critical” that could lead to remote code execution (RCE).
Critical Remote Code Execution (RCE) Vulnerability
The most …
Published: December 31, 2025
Tags:
IBM API Connect,
CVE-2025-13915,
vulnerability,
authentication,
security patch
Category:
vulnerabilities

IBM has disclosed details about a critical security flaw in its API Connect product that could allow remote attackers to gain unauthorized access to the application.
Vulnerability Details
The vulnerability, identified as CVE-2025-13915, has received a score of 9.8 out of 10.0 in the CVSS rating …
Published: December 30, 2025
Tags:
SmarterMail,
CVE-2025-52691,
CER,
vulnerability,
mail software
Category:
vulnerabilities

The Cyber Security Agency of Singapore (CSA) has issued an alert regarding a major security flaw in the SmarterTools SmarterMail email software. This vulnerability, with a CVSS score of 10.0, could be exploited to achieve remote code …
Published: December 26, 2025
Tags:
MuddyWater,
APT,
cyberespionage,
MuddyViper,
fooder
Category:
investigación-de-amenazas
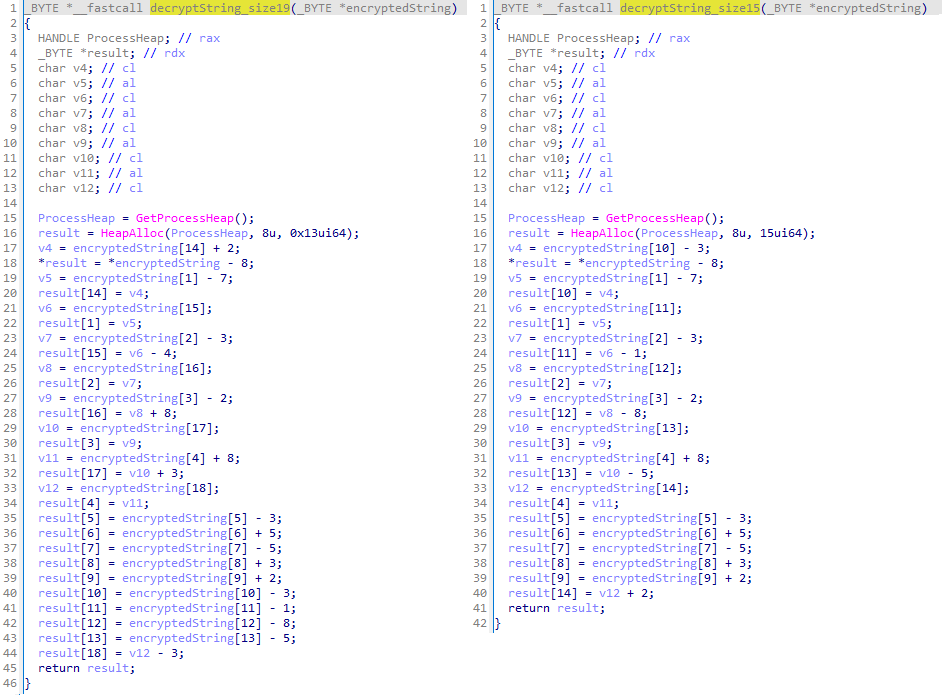
ESET researchers have discovered new activities of the Iran-aligned cyber espionage group MuddyWater (also known as Mango Sandstorm or TA450). This campaign primarily targets organizations in Israel and, in one confirmed case, Egypt, showing significant evolution in their technical and tactical …
Published: December 23, 2025
Tags:
n8n,
vulnerability,
CVE-2025-68613,
remote code execution,
patch management
Category:
vulnerabilities

A critical security vulnerability has been revealed in the n8n workflow automation platform. The flaw, if successfully exploited, could result in arbitrary code execution under certain circumstances.
The vulnerability, tracked as CVE-2025-68613, has a CVSS score of 9.9 out of 10.0, underscoring its …
Published: December 23, 2025
Tags:
supply chain security,
identity access management,
third-party risk,
zero trust,
data breaches
Category:
gestión-de-identidad-y-acceso
The Supply Chain: A Blind Spot in Identity Security
Security breaches often originate at the weakest link in the chain, and increasingly, this entry point is third-party access. Suppliers, contractors, and partners require access to internal systems to operate, but these permissions become …
Published: December 22, 2025
Tags:
phishing,
smishing,
online scams,
cybersecurity,
consumer safety,
christmas season
Category:
concienciación-en-seguridad
The holiday shopping season has brought with it a notable increase in cyber threats targeting consumers. According to recent data, there has been an 86% increase in malicious websites impersonating postal services in the last month. This trend underscores the growing risk for consumers awaiting …
Published: December 22, 2025
Tags:
Nezha,
post-exploitation,
evasion,
RAT,
threat hunting
Category:
pruebas-de-penetración
A legitimate and widely used open source server monitoring tool has been repurposed by attackers to gain complete remote control of compromised systems.
According to findings from the Ontinue Cyber Defense Center, the activity involves Nezha, a popular monitoring platform that offers …
Published: December 22, 2025
Tags:
Coupang,
data breach,
South Korea,
insider threat,
data encryption,
Penta Security
Category:
protección-de-datos
Coupang, South Korea’s leading e-commerce platform, has revealed a massive data breach affecting 33.7 million customer accounts, equivalent to nearly two-thirds of the Korean population. This incident has become the largest e-commerce security event in the country’s history and could …
Published: December 22, 2025
Tags:
cyber-attack,
DXS International,
NHS,
Devman,
data breach
Category:
incident-response
DXS International, a technology supplier to England’s National Health Service (NHS), has officially confirmed a cyber-attack on its systems. The incident, which was discovered on December 14, affected the company’s office servers.
In a filing to the London Stock Exchange on December 18, …
Published: December 22, 2025
Tags:
nissan,
red-hat,
data-gap,
crimson-collective,
shinyhunters
Category:
casos-de-estudio
Nissan Motor Co. Ltd. has confirmed that thousands of its customers’ information has been compromised following a data breach at its software provider Red Hat in September.
Nissan, a major automaker, reported that it was indirectly impacted by the security incident at the American company Red …
Published: December 22, 2025
Tags:
ransomware,
critical infrastructure,
Romania,
incident response,
BitLocker
Category:
respuesta-a-incidentes
Romania’s national water management authority, Romanian Waters (Administrația Națională Apele Române), confirmed being the victim of a ransomware attack during the weekend of December 20, 2025.
According to the National Cybersecurity Directorate (DNSC), the incident affected approximately …
Published: December 20, 2025
Tags:
aragua train,
jackpotting,
ploutus,
malware,
atm security
Category:
análisis-de-malware

The U.S. Department of Justice (DoJ) has announced the indictment of 54 individuals for their alleged involvement in an automated teller machine (ATM) “jackpotting” scheme that diverted millions of dollars. The large-scale conspiracy involved the use of Ploutus malware to force ATMs across the …
Published: December 20, 2025
Tags:
tls-callbacks,
dlls,
malware-analysis,
static-analysis,
dynamic-analysis
Category:
análisis-de-malware
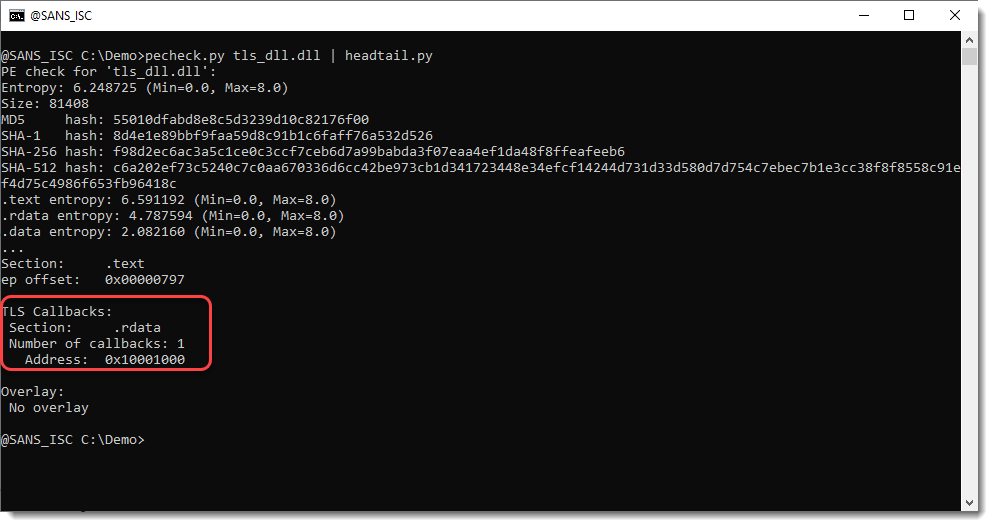
What are TLS Callbacks?
Thread Local Storage (TLS) is a Windows operating system mechanism that allows each thread in a process to have its own copy of specific variables. To support this, Windows PE (Portable Executable) executable files contain a TLS directory (IMAGE_TLS_DIRECTORY). This …
Published: December 20, 2025
Tags:
dma,
uefi,
iommu,
vulnerabilities,
firmware,
cve
Category:
vulnerabilities
A security vulnerability has been identified in specific motherboard models from leading manufacturers such as ASRock, ASUSTeK Computer, GIGABYTE and MSI. This flaw leaves systems susceptible to Direct Memory Access (DMA) attacks during the early boot phase, affecting architectures that implement …
Published: December 20, 2025
Tags:
HPE,
OneView,
vulnerability,
CER,
CVE-2025-37164,
patch
Category:
vulnerabilities

Hewlett Packard Enterprise (HPE) has announced the resolution of a maximum severity security vulnerability in its OneView software. The flaw, if successfully exploited, could allow remote code execution.
The critical vulnerability has been identified as CVE-2025-37164 and has a CVSS score of 10.0. …
Published: December 20, 2025
Tags:
WhatsApp,
frauds,
social engineering,
prevention,
cybersecurity
Category:
concienciación-en-seguridad

PTA Alert on the Increase in Fraud and Hacking on WhatsApp
Pakistan Telecommunication Authority (PTA) has issued an alert to mobile users regarding the increasing number of hacking and cyber fraud incidents through WhatsApp. Scammers are using social engineering tactics to trick people into gaining …
Published: December 20, 2025
Tags:
cybersecurity,
threats,
attack tactics,
threat intelligence,
persistent threats
Category:
inteligencia-de-amenazas

This week’s ThreatsDay newsletter highlights the continued adaptation of attackers, who are reconfiguring existing tools and finding new angles of attack on familiar systems. Small tactical changes are adding up quickly, suggesting possible directions for future security breaches.
Constantly …
Published: December 20, 2025
Tags:
watchguard,
fireware-os,
cve-2025-14733,
vulnerability,
patch-management
Category:
vulnerabilities

WatchGuard has issued a security alert and released patches to address a critical vulnerability in its Fireware operating system that the company has confirmed has been actively exploited in real-world attacks. The vulnerability, identified as CVE-2025-14733, affects IKEv2 VPN configurations and …
Published: December 18, 2025
Tags:
Cisco,
AsyncOS,
CVE-2025-20393,
APT,
UAT-9686,
Zero-Day
Category:
vulnerabilities

Cisco has issued an alert regarding a maximum severity zero-day vulnerability in its Cisco AsyncOS software. This flaw has been actively exploited by an advanced persistent threat (APT) actor with ties to China, dubbed UAT-9686, in attacks targeting Cisco Secure Email Gateway and Cisco Secure Email …
Published: December 18, 2025
Tags:
Kimsuky,
DocSwap,
malware,
phishing,
Android,
threat-intelligence
Category:
inteligencia-de-amenazas
North Korean threat group Kimsuky has been linked to a new cyberattack campaign that uses QR codes to distribute a new variant of the DocSwap Android malware. Attackers are using phishing sites that imitate South Korean logistics company CJ Logistics to trick victims.
Distribution and Deception …
Published: December 17, 2025
Tags:
CMMC,
ISACA,
DoD,
compliance,
cybersecurity,
defense
Category:
cumplimiento
The US Department of Defense (DoD) has designated ISACA as the global credentialing authority for the Cybersecurity Maturity Model Certification (CMMC) program. This designation seeks to ensure that defense contractors meet strict cybersecurity standards.
The CMMC program, introduced by DoD in …
Published: December 17, 2025
Tags:
Jewelbug,
Ink Dragon,
APT,
threat intelligence,
Shadow Pad,
FINALDRAFT,
cybersecurity
Category:
inteligencia-de-amenazas

The threat group known as Jewelbug, also tracked by Check Point Research as Ink Dragon, has intensified its attacks against government targets in Europe since July 2025. Although the actor, aligned with China and active since at least March 2023, continues to attack entities in Southeast Asia and …
Published: December 17, 2025
Tags:
botnet,
kimwolf,
DDoS,
Android security,
threat-research
Category:
investigación-de-amenazas

The Kimwolf botnet, a new distributed denial of service (DDoS) threat, has recruited a massive army of at least 1.8 million infected devices, primarily Android-based TVs, set-top boxes, and tablets. According to research by QiAnXin XLab, the botnet is associated with the infamous AISURU botnet. …
Published: December 11, 2025
Tags:
google-chrome,
vulnerabilities,
zero-day,
cve,
patch-management,
security
Category:
vulnerabilities
Google released a security update for Chrome on December 10, patching three new vulnerabilities, including a high-severity one that is being actively exploited in the wild. This vulnerability represents the eighth Chrome zero-day exploited in 2025.
The High Severity Zero-Day Vulnerability
Google …
Published: December 10, 2025
Tags:
WinRAR,
vulnerabilities,
CVE-2025-6218,
threat intelligence,
CISA
Category:
vulnerabilities

CISA warns about WinRAR vulnerability
The US Cybersecurity and Infrastructure Security Agency (CISA) has added a vulnerability affecting WinRAR compression software to its catalog of Known Exploited Vulnerabilities (KEV), citing evidence of active exploitation.
The vulnerability, tracked as …
Published: December 10, 2025
Tags:
vulnerabilities,
patches,
Fortinet,
Ivanti,
SAP,
cybersecurity
Category:
vulnerabilities
Fortinet, Ivanti, and SAP have released updates to address critical security flaws in their products. These vulnerabilities could allow authentication bypass or remote code execution if successfully exploited.
Fortinet Critical Vulnerabilities (CVE-2025-59718 and CVE-2025-59719)
Fortinet has …
Published: December 9, 2025
Tags:
artificial intelligence,
cyber attacks,
saas security,
oauth,
identity management,
zero trust,
threat intelligence,
gtg-1002
Category:
inteligencia-de-amenazas

The GTG-1002 Attack: The First Autonomous Cyberspace Campaign
In November 2025, Anthropic revealed details of an unprecedented cyberespionage campaign, dubbed GTG-1002. This was the first time a case of an artificial intelligence (AI) agent orchestrating real-world intrusions with minimal human …
Published: December 9, 2025
Tags:
CastleLoader,
GrayBravo,
MaaS,
threat-intelligence,
malware-analysis,
phishing,
logistics
Category:
inteligencia-de-amenazas

Recent research has revealed the existence of four distinct threat activity groups that are leveraging a malware loader known as CastleLoader. This evidence reinforces previous assessment that the tool is offered to other cybercriminals under a malware-as-a-service (MaaS) model.
The threat actor …
Published: December 6, 2025
Tags:
vulnerabilities,
artificial intelligence,
SDI,
prompt injection,
CER,
DevSecOps,
application security
Category:
vulnerabilities

A recent investigation has revealed more than 30 security vulnerabilities in several Integrated Development Environments (IDEs) powered by artificial intelligence (AI). These flaws, collectively called “IDEsaster”, combine prompt injection primitives with legitimate IDE features to …
Published: December 5, 2025
Tags:
cloudflare,
CDN,
distribution network,
service drop,
network security
Category:
seguridad-de-red
Cloudflare content delivery network (CDN) has experienced a new outage that has affected numerous websites globally. The failure, which occurred shortly before 10 a.m., coincided with a scheduled maintenance operation at the company’s data center in Detroit.
Affected Websites and Recurrence …
Published: December 5, 2025
Tags:
CVE-2025-55182,
React2Shell,
Earth Lamia,
Jackpot Panda,
AWS,
Threat Intelligence,
CER
Category:
inteligencia-de-amenazas

Two hacking groups linked to China have been detected weaponizing the newly disclosed vulnerability in React Server Components (RSC), known as React2Shell. The exploit was observed just hours after the existence of the flaw was made public, underscoring how quickly threat actors integrate new …
Published: December 5, 2025
Tags:
spyware,
predator,
intellexa,
zero-day,
vulnerabilities,
threat-intelligence,
malware-analysis
Category:
análisis-de-malware

A joint investigation by Amnesty International, Haaretz, Inside Story and Inside IT has revealed that the human rights lawyer from Balochistan province, Pakistan, was the target of Intellexa’s Predator spyware. This incident marks the first time that a member of civil society in Pakistan has …
Published: December 4, 2025
Tags:
ddos,
aisuru,
botnet,
threat-intelligence,
cloudflare
Category:
inteligencia-de-amenazas

Cloudflare has announced the detection and mitigation of a distributed denial of service (DDoS) attack that peaked at 29.7 terabits per second (Tbps), the largest ever recorded by the company. The attack, lasting 69 seconds, was launched by the botnet for hire known as AISURU.
The AISURU Botnet: …
Published: December 4, 2025
Tags:
GhostFrame,
phishing,
Barracuda,
phishing attack,
security-email
Category:
investigación-de-amenazas
A new phishing framework called GhostFrame, built around a stealthy iframe architecture, has been linked to more than a million attacks, cybersecurity experts at Barracuda have found.
This attack kit distinguishes itself from known Phishing-as-a-Service (PhaaS) offerings by its innovative approach …
Published: December 4, 2025
Tags:
GoldFactory,
Android malware,
Gigaflower,
mobile scams,
Group-IB
Category:
análisis-de-malware

Financially motivated cybercriminal group GoldFactory has launched a new wave of attacks targeting mobile users in Indonesia, Thailand and Vietnam. Attackers are using a government spoofing technique to distribute legitimate banking applications modified with malware.
The activity, observed since …
Published: December 4, 2025
Tags:
Silver Fox,
ValleyRAT,
SEO poisoning,
Threat Intelligence,
False Flag
Category:
inteligencia-de-amenazas
The cybercriminal group known as Silver Fox has been identified orchestrating a “false flag” operation to imitate a Russian threat group. This tactic seeks to camouflage its attacks directed at organizations in China.
The SEO poisoning campaign uses Microsoft Teams lures to trick …
Published: December 3, 2025
Tags:
CVE-2025-12744,
ABRT,
command injection,
privilege escalation,
vulnerability
Category:
vulnerabilities
Vulnerability Description
CVE-2025-12744 is an OS Command Injection vulnerability found in the Automatic Bug Reporting Tool (ABRT) daemon.
Technical Details
- The ABRT daemon copies up to 12 characters from untrusted user-supplied input.
- These characters are inserted directly into a shell command: …
Published: December 3, 2025
Tags:
vulnerability,
CVE-2025-9491,
windows,
patch-management,
threat-intelligence
Category:
vulnerabilities

Microsoft has quietly fixed a security vulnerability that has been exploited by multiple threat actors since 2017. The fix was included in the November 2025 Patch Tuesday updates.
The vulnerability, tracked as CVE-2025-9491 (CVSS score: 7.8/7.0), is a “misinterpretation of the Windows …
Published: December 3, 2025
Tags:
Salty2FA,
Tycoon2FA,
Phishing,
Threat Intelligence,
Malware Analysis,
Storm-1747
Category:
investigación-de-amenazas
Phishing kits typically have distinctive signatures in their delivery methods and infrastructure, making attribution easier. However, analysts have recently observed an overlap between two phishing kits such as Salty2FA and Tycoon2FA, marking a significant change that complicates detection.
ANY.RUN …
Published: December 3, 2025
Tags:
Water Saci,
banking trojan,
WhatsApp,
malware
Category:
threat-intelligence

The threat actor Water Saci is evolving its tactics, now employing a sophisticated infection chain that uses HTA files and PDFs to propagate a worm. This worm deploys a banking trojan via WhatsApp, targeting users in Brazil.
- The attackers have shifted from PowerShell to a Python-based variant to …
Published: December 2, 2025
Tags:
MuddyWater,
APT42,
Charming Kitten,
Iran,
cyber espionage,
MuddyViper,
Israel,
threat-intelligence
Category:
inteligencia-de-amenazas

Threat actors linked to the Iranian state have launched a new series of attacks against Israeli entities in various sectors, deploying a previously undocumented backdoor known as MuddyViper. The activity has been attributed to MuddyWater (also known as Mango Sandstorm or TA450), a hacking group …
Published: December 1, 2025
Tags:
Avast,
Free Antivirus,
Vulnerability,
CVE-2025-3500,
Privilege Escalation,
Kernel Security
Category:
vulnerabilities

Security researchers have revealed a critical vulnerability in Avast Free Antivirus that could allow attackers to gain elevated system privileges and execute malicious code with kernel-level access.
The vulnerability, tracked as CVE-2025-3500, received a high CVSS score of 8.8 and was made public …
Published: December 1, 2025
Tags:
India,
Sanchar Saathi,
cybersecurity app,
smartphone mandate,
digital security,
pre-installed app,
regulatory compliance
Category:
regulatorio

India’s telecom ministry has issued a directive requiring major mobile device manufacturers to pre-install a government cybersecurity app, Sanchar Saathi, on all new phones sold in the country. According to reports, the application cannot be deleted or disabled by users.
The directive, issued …
Published: November 28, 2025
Tags:
doxxing,
online security,
privacy,
cyberbullying,
family security,
security-awareness
Category:
concienciación-en-seguridad
The digital world offers many opportunities for self-expression and development, but it is also a space where disagreements can escalate quickly, and bullying, harassment and revenge are present. Doxxing is a leading form of online retaliation that can have a significant impact on the mental health …
Published: November 28, 2025
Tags:
npm,
malware,
contagiou-interview,
threat-intelligence,
north-korea,
ottercookie,
golangghost
Category:
inteligencia-de-amenazas

North Korean threat actors responsible for the “Contagious Interview” campaign have flooded the npm registry with 197 additional malicious packages since last month. According to a Socket analysis, these packages have accumulated more than 31,000 downloads and are designed to distribute …
Published: November 28, 2025
Tags:
microsoft-teams,
vulnerabilities,
cloud-security,
threat-intelligence,
microsoft-defender
Category:
vulnerabilities

Ontinue security researchers have discovered a “cross-tenant blind spot” in Microsoft Teams that allows attackers to bypass Microsoft Defender for Office 365 protections using the guest access feature.
The problem is that when a user operates as a guest in an external tenant, their …
Published: November 28, 2025
Tags:
pypi,
supply chain,
python-security,
vulnerabilities,
domain-takeover
Category:
vulnerabilities

Cybersecurity researchers have discovered vulnerable code in outdated Python packages that could pave the way for a supply chain compromise attack on the Python Package Index (PyPI) via a domain takeover technique.
Software supply chain security company ReversingLabs identified the vulnerability in …
Published: November 27, 2025
Tags:
mattermost,
cve-2025-12421,
account takeover,
vulnerability,
authentication
Category:
vulnerabilities

Mattermost Critical Vulnerability Summary
A default configuration in Mattermost, an open source collaboration platform used by enterprises and government agencies, exposes deployments to critical Account Takeover risk. The vulnerability, identified as CVE-2025-12421, allows an attacker, via a …
Published: November 26, 2025
Tags:
cybersecurity,
incident-response,
ransomware,
NCSC,
local authorities
Category:
respuesta-a-incidentes
Multiple local authorities in London are dealing with a serious cybersecurity incident, it has recently emerged. The Royal Borough of Kensington and Chelsea (RBKC) and Westminster City Council (WCC) issued a statement saying they are responding to an incident identified on Monday morning.
The …
Published: November 26, 2025
Tags:
romcom,
socgholish,
mythic-agent,
grunt,
cyber espionage,
russian-threats,
threat-intelligence
Category:
inteligencia-de-amenazas

Threat actors linked to the RomCom group have been observed using the SocGholish JavaScript loader to deliver the Mythic Agent to a US-based civil engineering company. This event marks the first time that a RomCom payload distributed through SocGholish has been detected.
The attack has been …
Published: November 25, 2025
Tags:
vulnerabilities,
data leak,
operational safety,
credentials,
JSON formatter,
CodeBeautify
Category:
vulnerabilities

New research has revealed that organizations in sensitive industries, such as governments, telecommunications, and critical infrastructure, are exposing passwords and credentials by pasting them into online code formatting and validation tools such as JSONformatter and CodeBeautify.
Cybersecurity …
Published: November 24, 2025
Tags:
cybersecurity,
flow bit,
vulnerability,
cloud computing,
kubernetes
Category:
ciberseguridad
Critical Bug Discovery in Fluent Bit
Cybersecurity researchers have discovered a set of critical vulnerabilities affecting Fluent Bit, a widely used telemetry agent with more than 15 billion deployments. These flaws highlight weaknesses in essential components that organizations use to move logs, …
Published: November 24, 2025
Tags:
DeepSeek,
Cybersecurity,
AI,
Vulnerability,
Geopolitics
Category:
Ciberseguridad

New research from CrowdStrike has revealed that the artificial intelligence (AI) reasoning model DeepSeek-R1 produces a significantly higher number of security vulnerabilities in response to requests containing topics considered politically sensitive by China.
The study, which assessed the impact …
Published: November 24, 2025
Tags:
Fluent Bit,
cybersecurity,
vulnerabilities,
CVE,
cloud security,
CER,
telemetry
Category:
Ciberseguridad

Security researchers at Oligo Security have discovered five vulnerabilities in Fluent Bit, a lightweight, open-source telemetry agent, that could be chained together to compromise and take control of cloud infrastructures.
Fluent Bit is widely used in enterprise environments, and successful …
Published: November 24, 2025
Tags:
cybersecurity,
data breach,
Iberia Airlines,
phishing,
supply chain attack
Category:
ciberseguridad
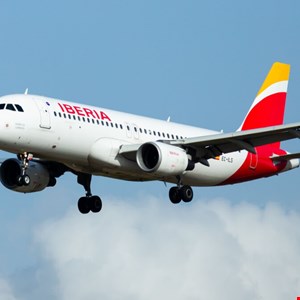
Security Alert: Iberia Airlines Reports Customer Data Breach
Iberia Airlines, part of the International Airlines Group (IAG) along with British Airways and Aer Lingus, has notified its customers about a security incident that compromised personal information. The data breach originated through an …
Published: November 24, 2025
Tags:
cybersecurity,
npm,
supply chain attack,
Sha1-Hulud,
malware,
GitHub,
TruffleHog
Category:
Ciberseguridad

Multiple security companies have warned of a second wave of attacks affecting the npm registry, reminiscent of the Shai-Hulud attack of September 2025. This new campaign, called Sha1-Hulud, has compromised hundreds of npm packages between November 21 and 23, 2025.
According to Wiz researchers, the …
Published: November 21, 2025
Tags:
Matrix Push C2,
Push Notifications,
C2 Platform,
Malware,
Cybersecurity
Category:
Ciberseguridad
A new command and control (C2) platform called Matrix Push C2 is being used by cybercriminals to distribute malware, taking advantage of a legitimate feature of web browsers: push notifications.
According to a report by BlackFrog, this malicious platform tricks users with fake system notifications, …
Published: November 21, 2025
Tags:
Salesforce,
Gainsight,
Cybersecurity,
OAuth,
Data gap,
ShinyHunters
Category:
Ciberseguridad

Security Alert for Unusual Activity in Gainsight Apps
Salesforce has issued a warning about detecting “unusual activity” related to apps published by Gainsight and connected to its platform. The company’s investigation suggests that this activity may have allowed unauthorized …
Published: November 21, 2025
Tags:
cybersecurity,
risk management,
supply chain,
BlueVoyant,
TPRM
Category:
ciberseguridad

Alarming Increase in Supply Chain Gaps
According to BlueVoyant’s annual State of Supply Chain Defense: Annual Global Insights Report 2025, an overwhelming majority of organizations (97%) have been negatively impacted by a supply chain breach. This data represents a significant increase …
Published: November 21, 2025
Tags:
WhatsApp,
cybersecurity,
data leak,
privacy,
vulnerability,
Goal
Category:
Ciberseguridad

Potentially Historic Massive Data Leak
Austrian researchers have revealed a mass enumeration vulnerability in WhatsApp that allowed the extraction of 3.5 billion user phone numbers. This finding highlights a security flaw in the app’s “contact discovery” feature, which, lacking …
Published: November 20, 2025
Tags:
WhatsApp,
cybersecurity,
social engineering,
session hijacking,
account takeover
Category:
Ciberseguridad
CTM360 has identified a rapidly expanding WhatsApp account hacking campaign, internally called HackOnChat. This campaign uses a network of deceptive authentication portals and phishing pages to target users around the world.
Attackers exploit WhatsApp’s familiar web interface and employ …
Published: November 19, 2025
Tags:
cybersecurity,
7-zip,
vulnerability,
CVE-2025-11001,
CER,
directories
Category:
Ciberseguridad
A newly disclosed security vulnerability affecting 7-Zip is being actively exploited in practice, according to an advisory issued by the United Kingdom’s NHS England Digital. The vulnerability allows remote attackers to execute arbitrary code on affected systems.
Vulnerability Details …
Published: November 19, 2025
Tags:
Dragon Breath,
Gh0st RAT,
RONINGLOADER,
cybersecurity,
APT,
malware,
cyber attack,
identity theft
Category:
Ciberseguridad
The cyber threat landscape targeting Chinese-speaking users has intensified with the detection of multiple malware campaigns. Two recent reports highlight the sophistication of threat actors using the Gh0st RAT remote access trojan, a malware known for its versatility.
One of the campaigns involves …
Published: November 19, 2025
Tags:
Dragon Breath,
Gh0st RAT,
RONINGLOADER,
Cybersecurity,
APT,
NSIS installers,
AV Evasion
Category:
Ciberseguridad
The threat group known as Dragon Breath, also tracked as APT-Q-27 and Golden Eye, has been detected using a multi-stage loader called RONINGLOADER to deliver a modified variant of the Gh0st RAT remote access Trojan. This campaign primarily targets Chinese-speaking users and uses Trojanized NSIS …
Published: November 19, 2025
Tags:
Fortinet,
FortiWeb,
CVE-2025-58034,
Cybersecurity,
OS Command Injection
Category:
Ciberseguridad

Fortinet has issued a crucial security alert about a new vulnerability in its FortiWeb product (a web application firewall), confirming that the flaw is already being actively exploited by attackers. This vulnerability, classified as medium severity, requires immediate action by system …
Published: November 19, 2025
Tags:
cybersecurity,
asus,
routers,
vulnerability,
wrthug,
botnet,
aicloud
Category:
Ciberseguridad
A newly discovered cyberattack campaign, dubbed Operation WrtHug, has compromised tens of thousands of ASUS routers that are end-of-life (EoL) or outdated. The operation has recruited these devices into a vast network of botnets.
Over the past six months, SecurityScorecard’s STRIKE team …
Published: November 19, 2025
Tags:
PlushDaemon,
EdgeStepper,
AitM,
cybersecurity,
APT,
SlowStepper
Category:
Ciberseguridad

The PlushDaemon threat actor has been identified using a new Go-based network backdoor, called EdgeStepper, to facilitate Adversary in the Middle (AitM) attacks. EdgeStepper has the ability to redirect all DNS queries to an external malicious node, diverting traffic from legitimate software update …
Published: November 19, 2025
Tags:
PlushDaemon,
EdgeStepper,
AitM,
Cybersecurity,
APT,
Attack on the Supply Chain,
SlowStepper,
China APT
Category:
Ciberseguridad
The threat group known as PlushDaemon has been detected using a new Go-based network backdoor, called EdgeStepper, to facilitate Adversary in the Middle (AitM) attacks and hijack software update mechanisms.
EdgeStepper, a previously undocumented implant, has been designed to reroute victims’ …
Published: November 19, 2025
Tags:
Ransomware,
Cybersecurity,
Q3 2025,
Credentials,
Zero-day,
Akira,
VPN
Category:
Ciberseguridad

The third quarter of 2025 saw a significant increase in ransomware attacks, with an 11% increase in data breach publications compared to the previous quarter. According to a report from Beazley Security, only three ransomware groups were responsible for the majority of cases (65%), with the primary …
Published: November 18, 2025
Tags:
AI,
cybersecurity,
privacy,
chatbots,
companion apps,
Sextortion
Category:
Ciberseguridad
The idea of entering into a romantic relationship with an artificial intelligence system, popularized by the movie “Her,” has moved from the realm of science fiction to a tangible reality thanks to the proliferation of generative AI and large-scale language models (LLM). Virtual …
Published: November 18, 2025
Tags:
doordash,
data breach,
social engineering,
cybersecurity,
pee,
security incident
Category:
ciberseguridad
Food delivery service DoorDash has confirmed that it suffered a data breach in October 2025, where some customers’ personal information was accessed. The company detailed that the incident was the result of a social engineering scam targeting one of its employees.
Details of the Data Breach …
Published: November 18, 2025
Tags:
AI,
fraud,
deepfakes,
cybersecurity,
identity verification
Category:
Ciberseguridad
Artificial intelligence (AI) technology is increasingly being adopted by fraudsters to commit new account fraud (NAF) and bypass even biometric checks. This is revealed by a new report from Entrust, which analyzed data from more than one billion identity verifications in 30 sectors and 195 …
Published: November 15, 2025
Tags:
cybersecurity,
vulnerabilities,
botnet,
xwiki,
ddos
Category:
ciberseguridad
The RondoDox botnet malware is actively exploiting unpatched XWiki servers via the critical vulnerability CVE-2025-24893 (CVSS 9.8), allowing arbitrary remote code execution.
🔍 CVE-2025-24893
Evaluation injection bug that allows any guest user to execute remote code via the /bin/get/Main/SolrSearch …
Published: August 7, 2025
Tags:
cybersecurity,
audit,
healthcare,
vulnerabilities
Category:
cybersecurity
A recent cybersecurity audit revealed critical vulnerabilities in the technological infrastructure of a recognized healthcare organization.
Published: May 8, 2025
Tags:
cybersecurity,
attack-surface,
security
Category:
cybersecurity
Practical recommendations to reduce your organization's digital attack surface: asset inventory, segmentation, patching, and continuous monitoring for stronger cybersecurity.